The matrix, working — not described
One record. Three roles.
“One platform, three pillars” is an architecture claim, not a slogan. Here is a single Chain of Custody and Certificate of Analysis, followed as it actually moves through Manufacturing, Testing, and Certification & Accreditation — the same object, never re-entered, never copied.
Manufacturing submits
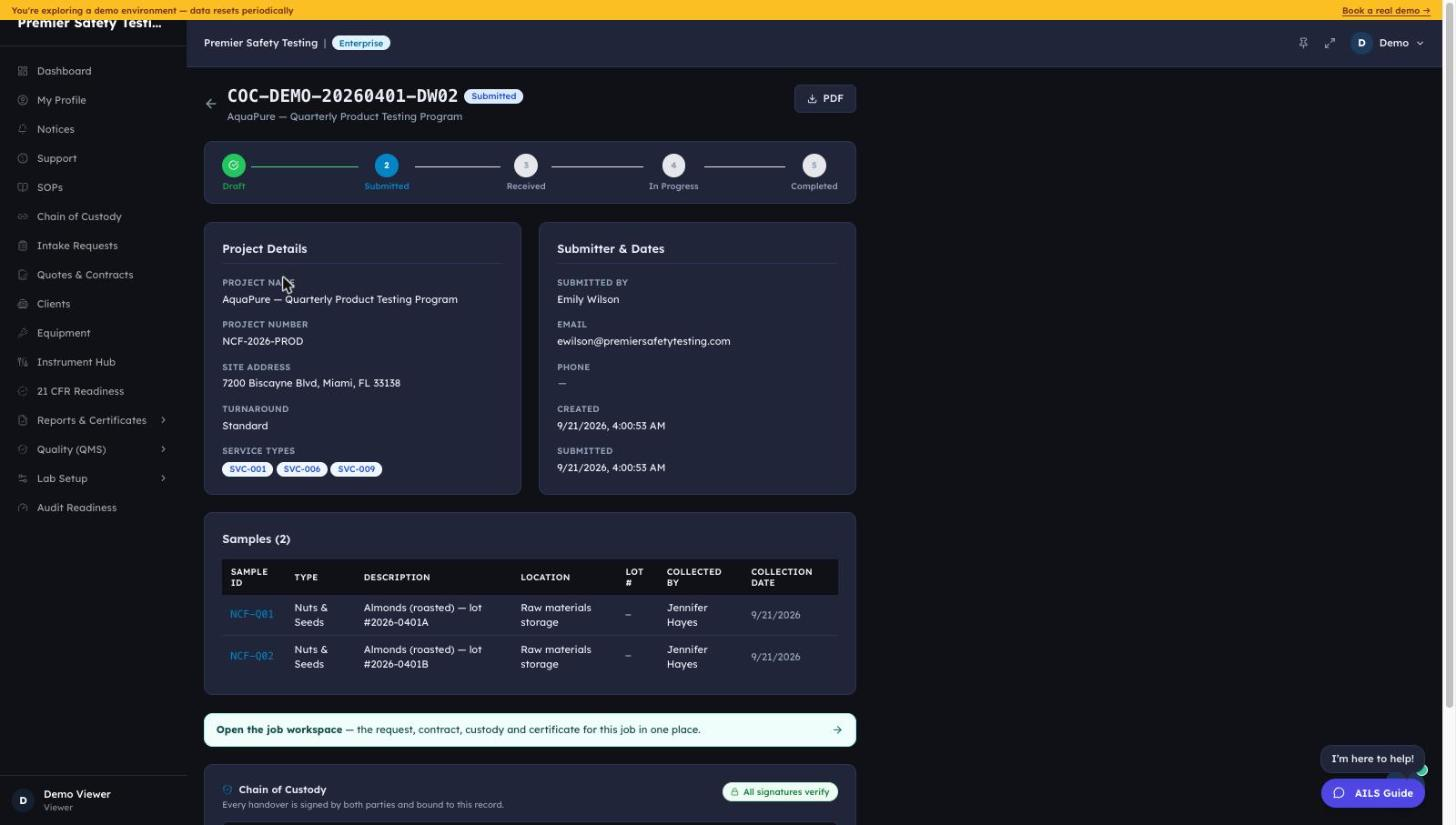
A production batch needs a result before it ships. The manufacturer opens a Chain of Custody record — sample type, collection details, requested test methods — and hands it to the lab. From this point the record has one identity: a single COC number that every later role reads from, not a copy of it.
What the manufacturer can do: submit intake, see status move from draft → submitted → received → in-progress → completed, and — once issued — download the resulting Certificate of Analysis. What the manufacturer cannot do: touch a result once it is entered, or see another tenant's samples. The COC is scoped to their own tenant database from creation.
Testing signs and issues
The lab receives the same COC — not a copy, the same record — runs the test method, enters results, and routes the Certificate of Analysis through issuance. Issuance requires re-authentication: the analyst re-enters their password, and the platform computes a SHA-256 hash over the finished document at that instant.
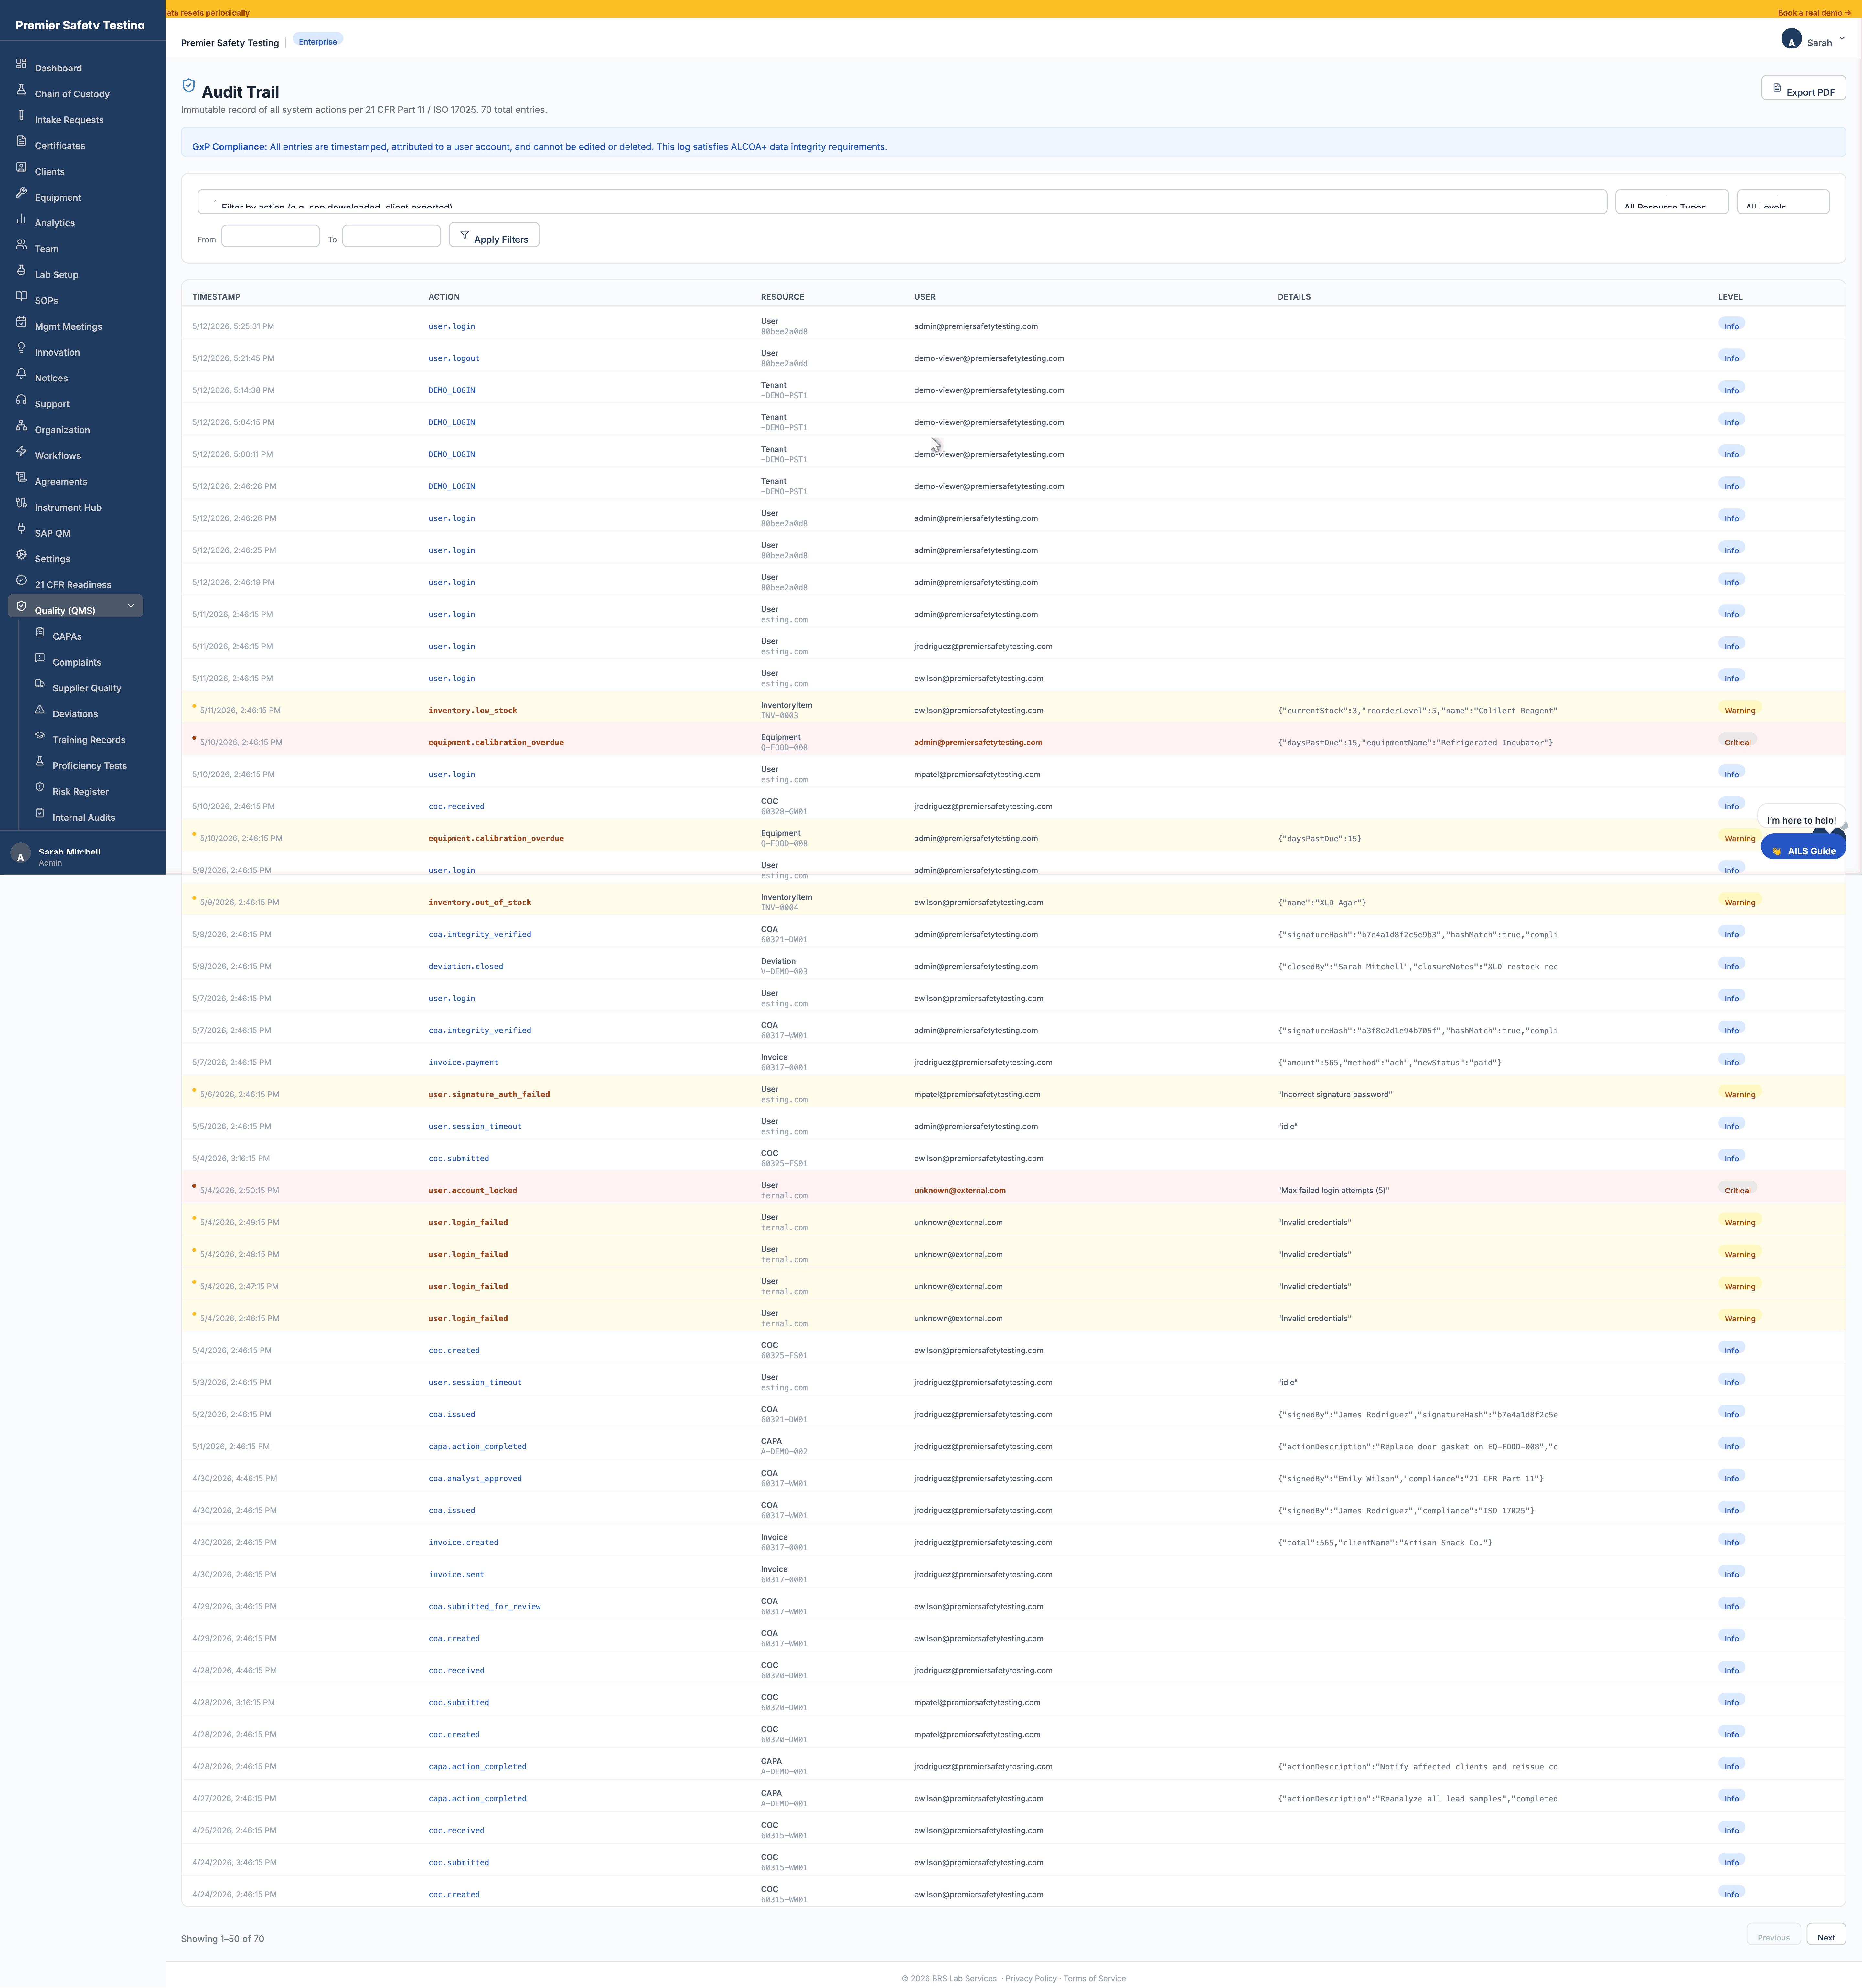
From that moment the COA is write-locked. No user, no admin, no platform operator has an edit path to a result after issuance — the audit trail shows exactly who signed, when, and what the document hash was, permanently.

Certification & Accreditation audits
A certification body, inspection body, or accreditation assessor doesn't receive a summary or a screenshot — they open the same tamper-evident record, with the same hash, and the same 5-year audit trail behind it. Nothing was re-entered for their benefit and nothing can have quietly drifted between the lab's copy and theirs, because there was never a second copy.
This is the concrete answer to "how do I know the certificate you're showing me is the one that was actually issued?" — the hash on the document and the hash in the audit trail are the same computation, checkable without calling the lab.
Pick your role, see the rest of the platform
Wherever you sit in this chain, the rest of it is built the same way — one governed record, permissioned by role.
See it work →